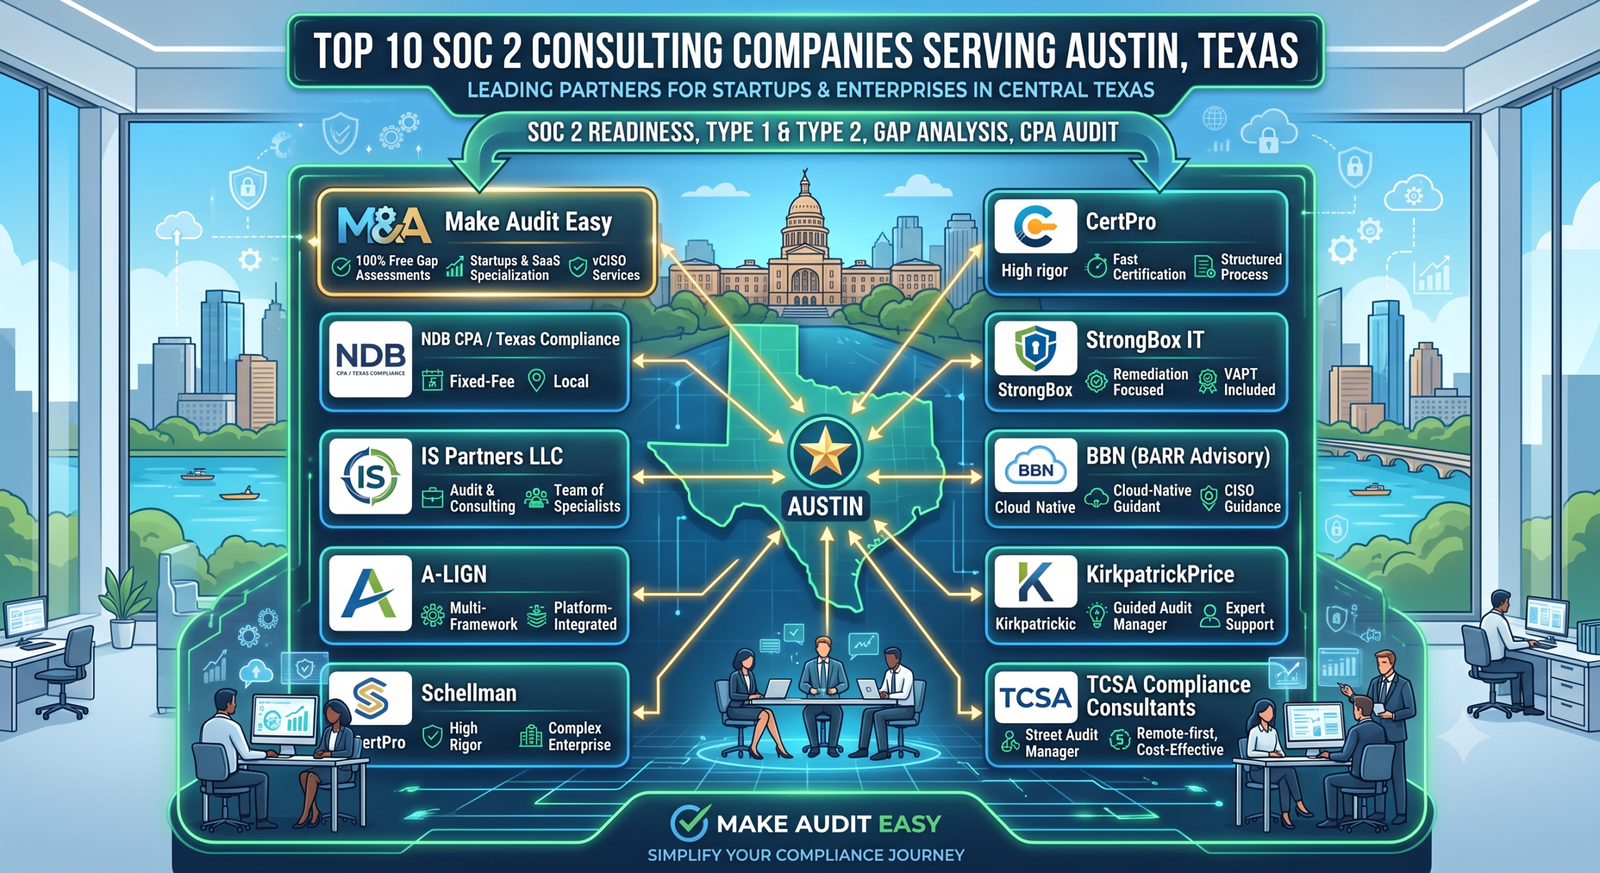
1. Make Audit Easy
- Best For: Startups, SaaS platforms, and tech companies looking for streamlined, end-to-end audit readiness and consulting.
- Key Services: SOC 2 Type 1 & Type 2 readiness, 100% free gap assessments, vCISO services, ISO 27001 mapping, and cybersecurity strategy consulting.
- Why Choose Them: Tailored specifically to simplify complex audit frameworks for growing businesses, offering hands-on guidance and policy creation without overwhelming internal teams.
2. NDB CPA / Texas Compliance
- Best For: Local Austin businesses seeking a Texas-based, licensed CPA firm specializing in fixed-fee SOC 2 audits.
- Key Services: SOC 1 & SOC 2 (Type 1 & Type 2) attestations, readiness assessments, PCI DSS, HIPAA, and policy template packs.
- Why Choose Them: Established presence in Austin with fixed-fee models, allowing predictable budgeting for technical and compliance audits.
3. IS Partners LLC
- Best For: Mid-market and enterprise organizations needing end-to-end consulting and final SOC attestation under one roof.
- Key Services: SOC 2 gap analysis, evidence collection, penetration testing, and certified CPA audit execution.
- Why Choose Them: 20+ years of experience with 100% U.S.-based senior auditors. They integrate seamlessly with modern automated compliance platforms.
4. A-LIGN
- Best For: Companies needing scale and multi-framework coverage (SOC 2, ISO 27001, HITRUST, PCI DSS).
- Key Services: SOC 2 Type 1 & Type 2 audits, automated evidence collection support, readiness assessments, and continuous compliance.
- Why Choose Them: One of the largest dedicated cybersecurity and compliance audit firms in the nation, highly recognized by enterprise enterprise buyers.
5. Schellman
- Best For: Enterprise SaaS, cloud architecture providers, and complex IT operations.
- Key Services: SOC 1, SOC 2, SOC 3, ISO 27001, FedRAMP, and HIPAA security assessments.
- Why Choose Them: A global CPA and assessment firm known for high-rigor audits, ideal for companies pitching to Fortune 500 clients.
6. CertPro
- Best For: Austin tech startups and SaaS providers looking for structured SOC 2 certification guidance.
- Key Services: Gap assessments, policy drafting, control implementation, and CPA coordination.
- Why Choose Them: Specializes in tech-focused compliance setups and helping companies navigate their first SOC 2 Type 1 or Type 2 journey efficiently.
7. StrongBox IT
- Best For: Emerging tech, healthtech, and cloud providers requiring technical remediation alongside SOC 2.
- Key Services: SOC 2 readiness assessments, gap analysis, vulnerability assessment & penetration testing (VAPT), and post-audit support.
- Why Choose Them: Strong focus on combining technical cybersecurity defenses (like penetration testing) with policy-level SOC 2 controls.
8. BBN (BARR Advisory)
- Best For: Cloud-native SaaS companies, startups, and high-growth mid-market organizations.
- Key Services: SOC 2 readiness consulting, CISO advisory, cloud security assessments, and audit attestations.
- Why Choose Them: Focuses on cloud-first environments (AWS, GCP, Azure) and reducing audit friction through automated workflows.
9. KirkpatrickPrice
- Best For: Educational-focused compliance guidance with dedicated audit direction.
- Key Services: SOC 2 readiness, penetration testing, HIPAA, PCI DSS, and custom security frameworks.
- Why Choose Them: Offers a guided “Online Audit Manager” framework with continuous auditor feedback to prevent last-minute surprises.
10. TCSA Compliance Consultants
- Best For: Cost-conscious Austin SaaS, healthtech, and hardware startups needing remote-first readiness consulting.
- Key Services: SOC 2 & ISO 27001 combined implementation, HIPAA mapping, and auditor coordination.
- Why Choose Them: Flexible, video-based consulting model designed to keep SOC 2 and ISO 27001 preparation costs predictable for early-stage companies.